October 1, 2026
The Situation
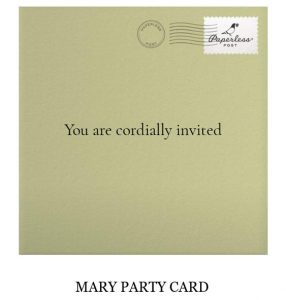
A client recently received an email containing what appeared to be a friendly invitation to a party.
The message was cordial, and the invitation looked legitimate enough that the client clicked on the invitation card.
Almost immediately, however, something didn't feel right.
Instead of ignoring the situation, the client contacted Cyber Intelligence Network and told us what had happened.
That quick phone call turned out to be extremely important.
What We Found
We immediately investigated the computer and discovered that clicking the invitation had resulted in ScreenConnect remote-access software being installed on the device.
ScreenConnect itself is a legitimate remote-support product commonly used by IT professionals. However, like many legitimate remote-access tools, it can also be abused by attackers.
If an unauthorized third party gains remote access to a computer, they may potentially be able to:
--View information displayed on the computer
--Access files available to the logged-in user
--Observe activity on the device
--Install additional software
--Capture sensitive information
--Use the compromised computer as a starting point for additional attacks
The concern wasn't that ScreenConnect existed.
The concern was that the client had not intentionally installed it or authorized anyone to remotely access the computer.
Our Response
Because the client reported the suspicious activity immediately, Cyber Intelligence Network was able to respond before the situation had an opportunity to develop further.
We identified the unauthorized remote-access software and removed it from the computer immediately.
The rapid response significantly reduced the opportunity for an unknown third party to establish persistent access or use the computer to cause further problems.
The Outcome
The suspicious software was removed before we observed evidence of the attacker using it to create additional problems.
Most importantly, the client recognized that something unusual had happened and contacted us instead of continuing to interact with the message or waiting to see what happened next.
That reaction made a difference.
The Lesson
Phishing attacks don't always look threatening.
Sometimes they look like:
--A party invitation
--A shared document
--A shipping notification
--An invoice
--A voicemail
--A password-reset request
--A message from someone you recognize
Attackers frequently rely on curiosity, familiarity, urgency, or trust to persuade someone to click.
This case also demonstrates an important cybersecurity principle:
Legitimate software can be used for malicious purposes.
Remote-access tools have valid business uses, but they should never appear unexpectedly on a computer.
What Should You Do If You Click on Something Suspicious?
If you click a link or attachment and immediately suspect something is wrong:
1. Stop interacting with it.
Don't continue clicking through prompts or entering usernames, passwords, financial information, or other data.
2. Contact your IT or cybersecurity provider immediately.
Don't wait until tomorrow to see whether something happens.
The earlier an incident is investigated, the greater the opportunity to contain it.
3. Tell your IT provider exactly what happened.
There is no benefit to hiding an accidental click.
Knowing what was clicked, what appeared on screen, and what happened afterward helps the security team investigate faster.
4. Follow the incident-response instructions you receive.
Depending on the situation, your IT provider may recommend disconnecting the computer from the network, changing credentials, reviewing account activity, scanning the device, or taking other precautions.
The CIN Takeaway
Cybersecurity technology is important, but employees also play a critical role in detecting attacks.
In this case, the client did something exactly right:
They recognized that something didn't look right and reported it immediately.
Employees shouldn't be afraid to report an accidental click.
The worst response to a suspicious event is often silence.
At Cyber Intelligence Network, we'd rather receive a call about something that turns out to be harmless than discover days later that an attacker has been quietly accessing a computer.
When something doesn't look right, report it immediately. Minutes can matter.
Cyber Intelligence Network
Cybersecurity-First Managed IT
Helping businesses and healthcare practices stay secure, productive, and prepared. Find out if your IT provider is leaving your business exposed, setup a discovery call with us.